Crypto Security News, October 2026: Implants, Hacks And Quantum
October 2026 crypto security news: Ledger's implant cases, Bitget's hack findings, bridge risk, quantum and AI key warnings, and app shutdown deadlines.
Key takeaways
- Ledger says every confirmed implant case involves devices sold through the reseller CryptoBilis, and its Genuine Check cannot detect added physical parts.
- Bitget says the hack that drained about $387.5 million came through a zero-day in third-party security products; its protection fund is a company promise with company terms, not insurance.
- Bridges remain one of the riskiest parts of crypto: the Kelp exploit in April 2026 cost about $292 million, and new verifier options shift some responsibility to app developers.
- Researchers warn that AI-assisted math or quantum computers could one day threaten today's wallet keys; the planning advice is to prepare, not to rush.
- When an app or network shuts down, the website closes before the contracts do, so know the official exit path and its deadline.
Security stories in September and October 2026 hit every layer a holder relies on: the hardware wallet in your drawer, the exchange you trade on, the bridges that move tokens between chains, the math behind your keys, and the apps that sit in front of smart contracts. Some of the losses were large. In most cases, the practical lessons are simple and old: buy devices from the source, know where your coins sit, and know the exit path before you need it.
Each section gives the date, what happened, why it matters and the open question. Facts are as of 15 October 2026. This is education, not advice on what to do with any specific coin.
| Story | Where the weak point was | Dates to know |
|---|---|---|
| Ledger implant cases | Devices tampered with before sale | Guidance issued 9 to 13 October |
| Bitget hack | Third-party security products at the exchange | Hack on 24 September |
| Kelp and CCIP 2.0 | Bridge verifier setup | Kelp exploit April; CCIP 2.0 on 28 September |
| Bunker mode and BIP-360 | Future attacks on wallet signatures | Forecasts and drafts only |
| Blur, Blast, Abstract | App and network shutdowns | Blast site route to 26 October; Blur 12 November; Abstract 15 December |
| Aztec zk.money | Early, unaudited code | Relaunched 29 September |
What do we know about the Ledger implant cases?
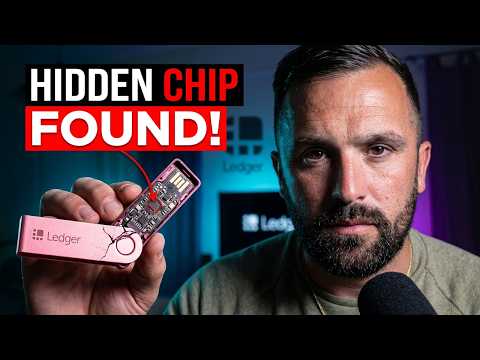
On 9 October 2026, Ledger told users who bought devices from the reseller CryptoBilis in the previous 90 days not to start setup, and anyone already set up to move to a new device with a new seed, The Block reported. On 10 October Ledger said one affected device contained “an unauthorized hardware implant”, per CoinDesk.
On 13 October, Ledger described how it worked: a chip inside the case read the 24-word phrase from the screen during setup and sent it out over a mobile network, CoinDesk reported. Ledger says its secure element and software were not modified. MediaMarkt Saturn paused Ledger sales in Germany after one customer reported an implant, The Block reported. Outside estimates of losses run up to $93.2 million; Ledger says it has not fully verified them.
Why it matters: Ledger’s buying guide says Genuine Check cannot detect added physical modifications. Where you buy matters. Our hidden chip checklist has the steps.
Open question: who tampered with the devices, and where in the supply chain.
What did Bitget say caused its hack?
On 24 September 2026, Bitget said about $351.6 million left its hot and warm wallets, later raised to $387.5 million after tracing, BleepingComputer reported. Bitget paused withdrawals, said balances “remain accurate” and said cold wallets were not affected. It later said attackers used a zero-day in third-party security products, per BleepingComputer and The Hacker News. Bitget has said it suspects North Korea; that is its suspicion, not a finding.
Bitget says it refilled its protection fund to more than $300 million. The fund page says Bitget reserves the right to assess each claim, subject to investigation results. It does not call the fund insurance.
Why it matters: exchange balances are a promise from the exchange. Withdrawals can stop for days even when balances are covered. We covered the XRP side in Bitget’s hack and exchange risk.
Open question: the final investigation results and how claims are handled.
Do Chainlink’s CCIP 2.0 and Vault Adapters reduce bridge risk?
They change who carries it. In April 2026, an exploit of Kelp DAO’s rsETH bridge cost about $292 million, The Block reported. The bridge ran with a single verifier, and LayerZero later said that setup for large transactions was a mistake, per ForkLog; responsibility is disputed.
On 28 September 2026, Chainlink launched CCIP 2.0, with a default committee of 16 independent node operators and optional extra verifiers. Chainlink’s own responsibility docs warn that unresponsive verifiers can stall transfers and that developers share accountability. On 8 October, Chainlink announced Vault Adapters, letting a vault on one network accept deposits from 80+ chains.
Why it matters: bridges have a long loss record, about $2 billion in 13 hacks in 2022 alone, per Chainalysis. More checks help, but no bridge is risk-free.
Open question: we found no deposit volumes or adapter audit reports on the pages we read.
What is Justin Drake’s “bunker mode” warning?
On 7 October 2026, Ethereum Foundation researcher Justin Drake called on the industry to plan for “bunker mode”, The Block reported. His view: AI-accelerated math could break the signature scheme most wallets use before quantum computers do, possibly in “months not years” in a worst case. He called for a controlled mass migration to fresh addresses, large holders first, and said “Don’t rush” and “Don’t panic either”. He was not claiming current cryptography is broken.
Vitalik Buterin took the risk seriously but warned that people have lost more in botched migrations than in hacks.
Why it matters: ethereum.org notes that an account’s public key is exposed once it has sent a transaction, and that no quantum computer today can break Ethereum’s cryptography. The trigger was OpenAI publishing 722 math manuscripts from an unreleased model on 6 October.
Open question: this is a researcher’s forecast, not an event. Watch for wallet software guidance.
What is Coinbase asking Bitcoin developers to do about quantum risk?
On 13 October 2026, Coinbase published a call to start post-quantum work now, saying “Bitcoin consensus changes and ecosystem migrations can take years”. It calls the post “an input to an open discussion, not a set of instructions”. Its asks include a hybrid signature option, a stateless fallback, and treating long-dormant coins as a separate problem. Coinbase says it holds about 5% of all bitcoin for clients, per CoinDesk.
The main proposal on the table is BIP-360, still a draft. Its authors say it is unclear when, or if, quantum computers able to break Bitcoin will arrive. NIST finalized its first post-quantum signature standards in August 2024.
Why it matters: a large custodian publicly asking for an early start shifts the debate. Nothing changes for holders today. Background: XRP and quantum signature risk.
Open question: whether a proposal reaches developer consensus.
What happens to Blur’s Blend loans when the website closes?
On 12 October 2026, Blur said its website will close on 12 November 2026, while its marketplace contracts stay on-chain, The Block reported. Its NFT lending product Blend stops matching new loans on 12 November; borrowers have until then to repay or let loans default. Blur says it will provide a tool afterward to help users withdraw assets from Blend, with no date given.
Paradigm’s original design note explains that if nobody refinances a loan when a lender exits, the borrower is liquidated and the lender takes the NFT. Monthly volume fell from about $1.43 billion in March 2023 to under $7 million in March 2026, per CoinDesk.
Why it matters: a website is one door to the contracts, not where your assets sit.
Open question: the date of the withdrawal tool, and how users reach the contracts after 12 November.
What did Blast and Abstract tell users about withdrawals?
On 2 October 2026, Blast, an Ethereum layer 2, said it is shutting down because “the economics of operating the chain no longer make sense”, The Block and CoinDesk reported. Users could withdraw through Blast’s interface until 26 October; after that, through the bridge contracts on Ethereum directly. Blast’s docs describe a prove step, a one-day challenge period and a claim, and say USDB comes out as DAI.
On 7 October, Abstract became the second layer 2 to announce a shutdown in a week, CoinDesk reported. Its migration page says the network closes on 15 December 2026 and unmigrated funds lose access.
Why it matters: shutdowns attract fake “migration” messages. Use only the official pages. See how exchange and app shutdowns work.
Open question: how smoothly direct contract withdrawals work after the website routes close.
What does Aztec’s zk.money hide, and what stays public?
On 29 September 2026, Aztec Labs relaunched zk.money, a self-custodial private payments wallet on the Aztec network, CoinDesk and The Block reported. Payments inside are private, but deposits from Ethereum still show the sender and amount, per Aztec’s docs.
The risk notes are plain. Aztec’s alpha page says no part of its stack is fully audited and bugs, including critical ones, are expected. In August, Aztec disclosed a proving flaw found on 27 July and said it cannot determine whether it was exploited, with a fix planned later in 2026. CoinDesk reports transaction caps below $2,500 and sanctions screening of deposit addresses.
Why it matters: privacy tools reduce what others can see, not every trail. Early, unaudited code carries real risk of loss.
Open question: the timing of the planned fix and a full audit.
What to watch next
- Ledger’s findings on where the CryptoBilis devices were tampered with.
- Bitget’s final investigation report and protection fund claims.
- 12 November 2026: Blur’s website and Blend new-loan cutoff.
- 15 December 2026: Abstract’s closing date.
- Any wallet guidance on post-quantum or “bunker mode” migrations.
A short self-check: where did you buy your hardware wallet, which of your coins sit on exchanges or bridges, and do you know the official exit path for each app you use?
Sources
- NIST Releases First 3 Finalized Post-Quantum Encryption Standards, National Institute of Standards and Technology
- Introducing CCIP Vault Adapters: Enabling 1-Click Deposits From Any Chain, Chainlink
- Alpha V5 Proving System Vulnerability, Aztec
- Best Practices To Securely Buy Your Ledger Signer, Ledger
- Protection Fund, Bitget
Frequently asked questions
How do I know if my Ledger was tampered with?
Ledger says confirmed cases involve devices bought through CryptoBilis. Its guidance is not to set up an unused CryptoBilis device, and if one is in use, to move assets to a new device with a new recovery phrase. Ledger never asks for your 24 words.
Is the Bitget protection fund insurance?
No. Bitget's own fund page says it reserves the right to assess each claim, subject to investigation results. It is a company fund with company terms.
Should I move my coins because of quantum computing?
The researchers quoted here advise planning, not rushing. Ethereum.org says no quantum computer today can break Ethereum's cryptography, and Vitalik Buterin warned that rushed migrations have lost people more than hacks.
What happens to my funds if a layer 2 network shuts down?
Funds usually remain in the bridge contracts on Ethereum. Blast and Abstract both published exit paths, but the easy website routes close on set dates, after which withdrawals are harder.
Education and commentary only, not financial advice. Crypto is volatile and you can lose money. Do your own research and speak to a qualified advisor before making investment decisions. Figures are as of October 28, 2026 and may have changed since.